VidAU Editorial · AI Search
How to Build an autonomous ai agent: Architecture, Tool Discovery, Security, and On‑Prem Options
Build an autonomous AI agent step by step. Learn ADK-style architecture (sense–plan–act), implement tool discovery to cut tokens, add security/governance, and compare self-hosted platforms like AutoGen, SuperAGI, and LaVague for on‑prem deployments.
By the VidAU Editorial Team · Reviewed before publishing
Build an autonomous AI agent that actually finishes work: start with an ADK sense–plan–act loop, add tool discovery for ai agents (search + execute, progressive), and run it on an on‑prem stack you control. This step‑by‑step playbook keeps costs, reliability, and risk in check.
Quick Summary
• An ADK sense–plan–act loop anchored by LLM reasoning and action tools is the most reliable path to a production autonomous ai agent.
• AutoGen, SuperAGI, and LaVague are strong open-source starting points for on‑prem builds, with Microsoft Copilot Studio as a managed or hybrid option.
• Tool discovery with MCP using search + execute and progressive discovery reduces context bloat, token cost, and failure modes.
• US enterprise teams in regulated environments benefit most from scoped credentials, audit logs, human checkpoints, and on‑prem deployment.
What Is an Autonomous AI Agent?
An autonomous AI agent is a software system that can pursue goals by sensing inputs, planning next steps, and taking actions via tools or APIs with minimal supervision. Unlike basic chatbots, agents maintain state, reason across steps, select tools dynamically, and self‑evaluate progress. ADKs (Agent Development Kits) formalize this into a repeatable sense–plan–act architecture.
Step-by-Step: Build an autonomous ai agent with an ADK loop
1) Define a narrow, high-value task domain
• Start with a bounded workflow (e.g., commerce ops triage, IT ticket routing) and clear success criteria.
• Write guardrails: allowed data, allowed tools, max steps, max spend.
2) Choose the reasoning and action layers
• Reasoning: Select an LLM for planning, reflection, and error handling.
• Actions: Expose capabilities as tools/APIs; consider Large Action Models (LAMs) when actions map well to complex, parameterized tasks.
• Memory/state: Use a lightweight store for goals, steps, artifacts, and tool results.
3) Implement the plan-and-act loop
• Sense: Parse the user goal and environment signals (docs, tickets, telemetry).
• Plan: Draft a step list with explicit tool calls and termination criteria.
• Act: Execute tools, capture outputs, and validate.
• Reflect: Compare outputs to goals, revise the plan, or escalate.
• Terminate: Stop on success, on safety triggers, or at step/spend limits.
4) Add human-in-the-loop (HITL) moments
• Insert approvals before irreversible or sensitive actions (e.g., refund issuance, data export).
• Provide diffs/summaries for fast human review, then continue autonomously.
5) Prepare for production
• Observability: Log prompts, tool inputs/outputs, decisions, and costs.
• Rollout: Start with low-risk canaries, then expand by segment or use case.
Suggested Visual: A simple ADK loop diagram showing Sense → Plan → Act → Reflect → Terminate with HITL checkpoints.
Implement tool discovery for ai agents with MCP
Tool discovery prevents loading every tool schema into the context window. Instead, the agent finds and loads only what it needs at runtime.
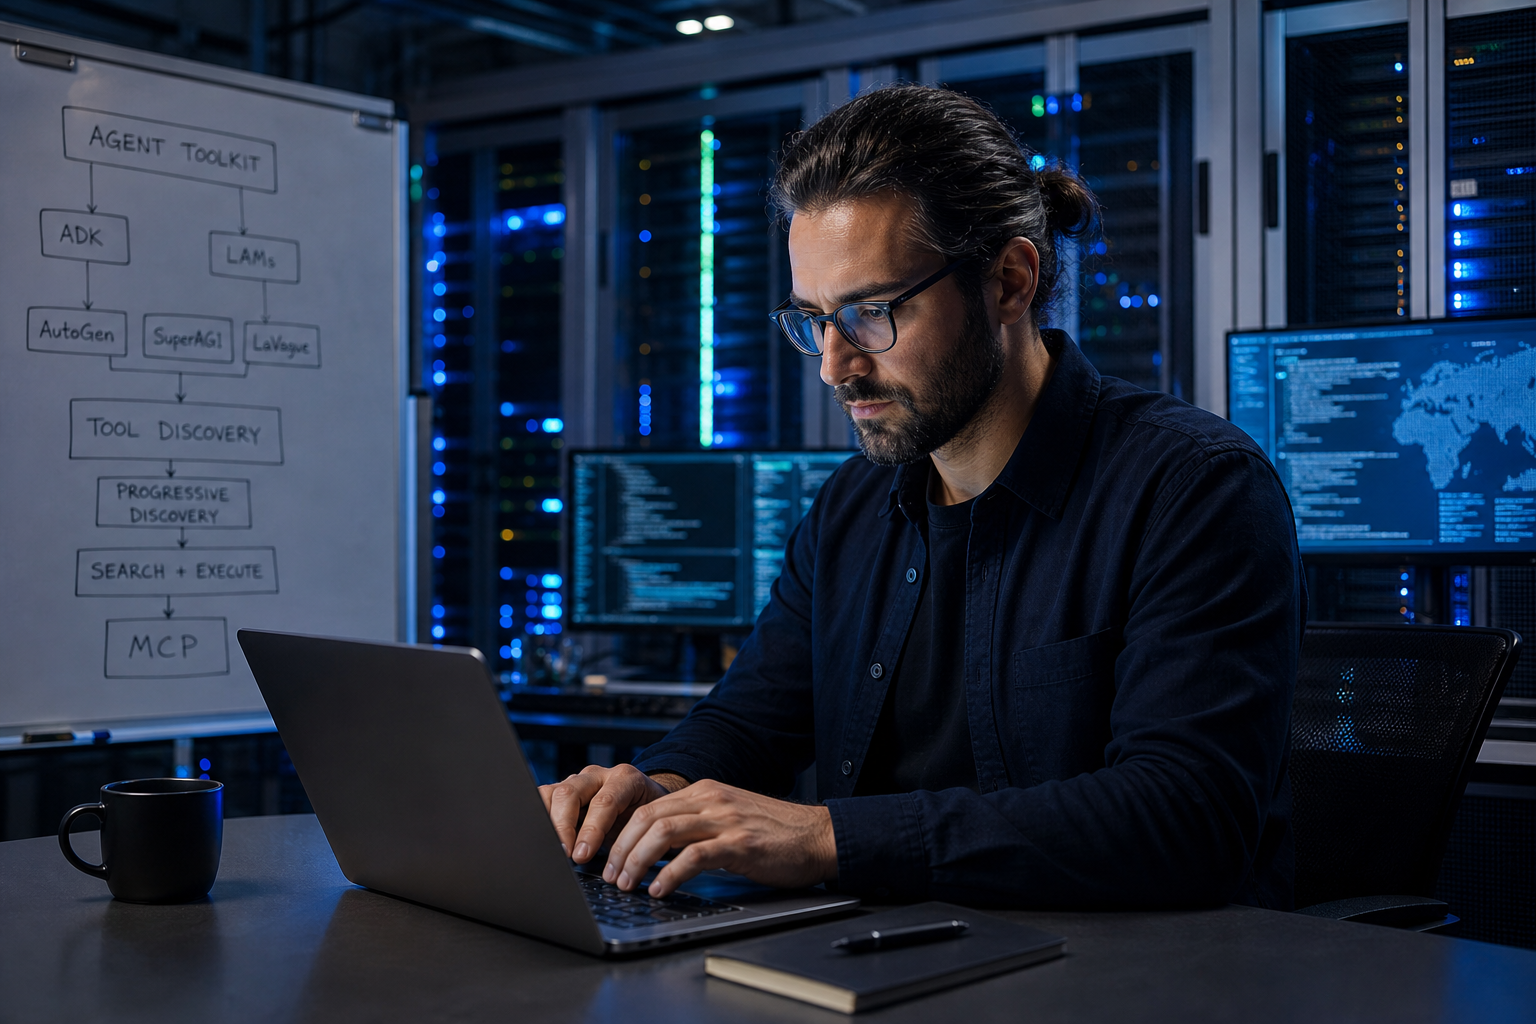
• Protocol: MCP (Model Context Protocol) standardizes how models discover and interact with external tool servers.
• Pattern 1: Search + Execute
• Search: Semantic search across a registry of tool descriptions.
• Fetch: Load only the top-matched tool schema.
• Execute: Call the tool, then iterate if needed.
• Pattern 2: Progressive tool discovery
• Step 1: list_domains to narrow the domain (e.g., billing, support, analytics).
• Step 2: list_tools within that domain.
• Step 3: get_tool_schema only for selected tools, then execute.
Practical tips
• Cache schemas for the session; evict after TTL to avoid drift.
• Penalize tools that recently failed to reduce retries.
• Normalize tool descriptions so search is consistent across providers.
• Log discovery decisions for offline analysis of misses and false positives.
Common mistakes to avoid
• Stuffing dozens of schemas up front (token bloat, higher confusion rate).
• Over-broad search queries; prefer goal + constraints + recent state.
• Skipping schema validation before execution.
Secure and govern your autonomous ai agent
Autonomy without guardrails creates risk. Bake in controls at every layer.
Application-layer defenses
• Prompt-injection resistance: Strip or sandbox untrusted content; use allowlists for instructions.
• Output scanning: Check tool outputs for malicious markup, unexpected URLs, or policy violations.
• HITL gates: Require approvals for sensitive actions or high-confidence thresholds.
Data and identity controls
• Scoped credentials: Per-tool, least privilege, short-lived tokens.
• PII handling: Redact, tokenize, or route through privacy filters; log access events.
• Data boundaries: Enforce tenant isolation and environment-specific endpoints.
Platform safeguards
• Egress policies: Restrict outbound domains and ports for tools.
• Auditability: Immutable logs of prompts, tool calls, and user approvals.
• Rate and spend limits: Cap requests, steps, and cost per task.
Governance and review
• Policy-as-code: Encode allowed tools, actions, and escalation rules.
• Independent evals: Red-team with prompt injection, data exfiltration, and tool abuse tests.
• Traceability: Preserve artifacts for compliance reviews.
IBM Technology explainers emphasize transparent safeguards and auditability; adopt those principles regardless of stack.
Key Takeaways
• Defend at input, action, and output layers.
• Scope credentials and redact PII by default.
• Log everything needed to explain decisions.
On‑prem and self‑hosted platforms to run agents
Below are example frameworks often used for on‑prem or hybrid builds. Validate fit, support, and licensing for your environment.
• Platform: AutoGen
Best fit: Multi-agent workflows
Notes: Event-driven, extensible agents
• Platform: SuperAGI
Best fit: Operational agent runners
Notes: Tooling, concurrent agents
• Platform: LaVague
Best fit: Web automation agents
Notes: World model + actions
• Platform: Microsoft Copilot Studio
Best fit: Managed or hybrid builds
Notes: Enterprise connectors, governance
Use these with your ADK design: plug in your planner, tool registry via MCP, and security controls outlined above.
KPIs, evaluation, and rollout strategy
Define success before scaling.
Core KPIs
• Task success rate: Completed goals without human fixes.
• Steps-to-completion: Planned vs. actual steps.
• Tool error rate: Invalid schema calls, auth failures.
• Token and runtime cost: Per task and per step.
• Autonomy ratio: Actions taken without human approval.
• Guardrail triggers: Blocks, approvals, policy hits.
Evaluation harness
• Scenario matrix: Simple, cross-domain, and multi-step tasks.
• Golden datasets: Fixed inputs with expected tools and outputs.
• Fault injection: Noisy inputs, stale schemas, and API outages.
• Replay tests: Validate improvements before production release.
Rollout
• Start with canaries and read-only agents (observe outcomes).
• Move to shadow mode (agent acts, results compared, no external effects).
• Graduate to controlled write access with HITL checkpoints.
Create With VidAU
Turn scripts, product URLs, and creative ideas into ad-ready video assets with a structured AI workflow.
Key takeaway
Final Thoughts
A dependable autonomous ai agent starts with an ADK sense–plan–act loop, adds tool discovery to stay lean and accurate, and ships with layered security and governance. Keep scope tight, measure relentlessly, and scale only after your evaluation harness shows stable gains.
Your next step: pick a single workflow, wire in MCP-based tool discovery (search + execute and progressive), stand it up on an on‑prem framework like AutoGen, SuperAGI, or LaVague, and enforce the security checklist from day one.
Frequently asked questions
What makes an autonomous ai agent different from a chatbot?
A chatbot answers prompts in a single turn, while an autonomous ai agent maintains state, plans across multiple steps, selects and executes tools or APIs, and self-evaluates progress. The agent’s loop includes sensing inputs, planning, acting, and reflecting, which enables it to complete tasks rather than just reply.
What is an Agent Development Kit (ADK) in this context?
An ADK is a structured approach or toolkit for building agents beyond chat. It formalizes a sense–plan–act loop, integrates reasoning models, tool interfaces, memory, and guardrails. Using an ADK-style design helps teams move from ad hoc scripts to maintainable, testable, and governable agent systems.
How do Large Action Models (LAMs) fit into agent design?
LAMs map complex, parameterized actions directly from model outputs to tool execution. They are useful when tasks involve rich, multi-argument functions or long action chains. In practice, combine an LLM for planning with LAM-backed tools for precise execution in domains with well-defined actions.
What is tool discovery, and why does it reduce token cost?
Tool discovery loads only the tools an agent needs at runtime rather than preloading all schemas into the context window. Using MCP with search + execute or progressive discovery narrows choices, reduces context size, cuts token usage, and improves reliability by avoiding tool confusion.
How does MCP (Model Context Protocol) help with agents?
MCP standardizes how models discover, describe, and call external tools via tool servers. It supports searching a registry, fetching schemas on demand, and executing actions with consistent interfaces. This reduces custom glue code and enables scalable, protocol-driven tool discovery for agents.
What security safeguards are essential for autonomous agents?
Adopt prompt-injection defenses, output scanning, scoped and short-lived credentials, PII redaction, and strict egress controls. Add audit logs for prompts and tool calls, set rate and spend limits, and require human approvals before sensitive or irreversible actions. Test with red-team scenarios regularly.
Which on‑prem platforms are common for running agents?
AutoGen, SuperAGI, and LaVague are frequently used open-source options for on‑prem or self-hosted deployments. Microsoft Copilot Studio can fit managed or hybrid scenarios. Choose based on your workflow needs, security posture, and operational preferences, and validate compatibility with MCP-style tool discovery.
How should I measure whether my autonomous ai agent is production-ready?
Track task success rate, steps-to-completion, tool error rate, token and runtime costs, autonomy ratio, and guardrail triggers. Use a scenario matrix, golden datasets, and replay tests. Promote from read-only to shadow mode to controlled write access only after stable KPI improvements.
Do I always need human-in-the-loop checkpoints?
For regulated or high-impact actions, yes. Insert approvals for sensitive changes, external communications, data exports, or financial operations. For low-risk tasks, you can relax checkpoints as confidence grows, but keep audit logs and rollback options in place.
How do I prevent token bloat as I add more tools?
Adopt tool discovery patterns. Use search + execute to shortlist tools and progressive discovery to load schemas only when necessary. Cache schemas during a session, normalize tool metadata, penalize failing tools, and cap max tools per step to contain context growth.